Platform
One record per device, in a workspace you own.
SMEDTEC OS is the regulatory operations workspace for manufacturers and brand owners of medical devices and IVDs: pathways, registrations, post-market work and the evidence behind them, hung off one record per device. Your workspace has its own document vault and immutable log, and an adviser sees only what you choose to share.
The product in 40 seconds · fictional demonstration data
01 · Product record
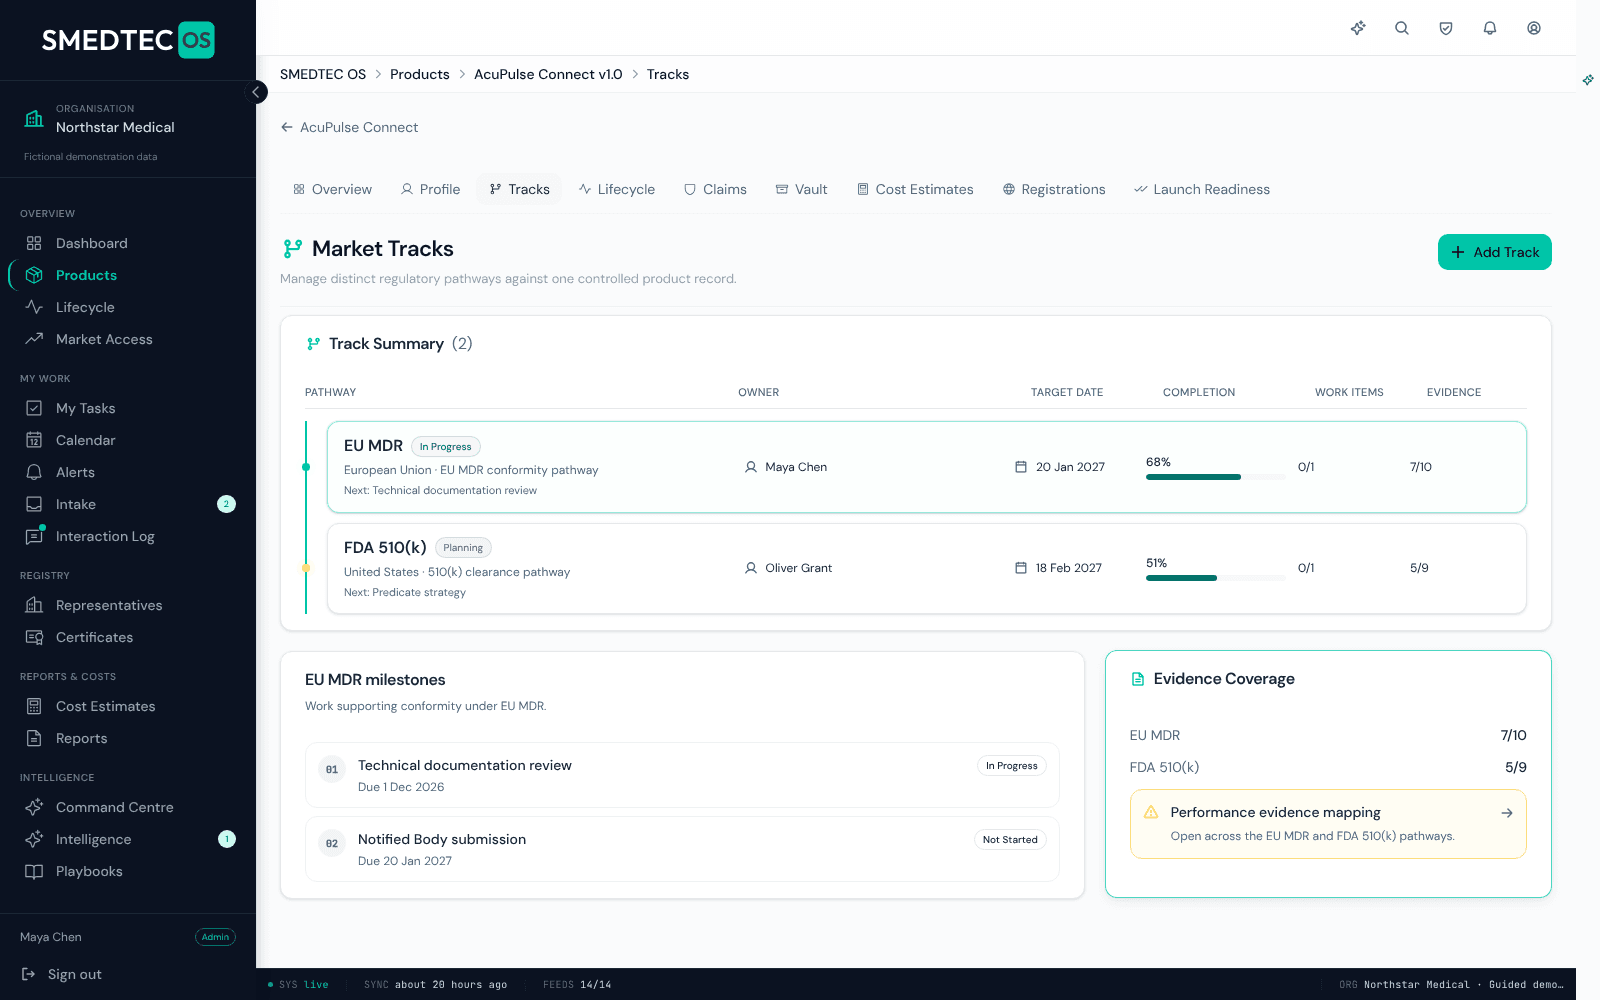
One record per device, and the pathways that hang off it
Define each device once, with its classifications, SKUs, target markets and lifecycle stage. Every submission, registration, post-market cycle and document hangs off that record.
One record per device
Classifications, SKUs, target markets and lifecycle stage, defined once
Pathways as tracked work
Phased work items with owners, due dates and dependencies, for EU MDR, IVDR, 510(k), De Novo, PMA, UKCA, MHRA, TGA, Health Canada and more
Launch readiness
A gate between launching and selling
Costs, certificates and dates
Cost estimates per market, certificates, a calendar, your own task queue and alerts
Real-world evidence for FDA
A source register, the relevance and reliability checklist and a protocol version log; no patient-level data
02 · Registrations and post-market
Every market, every renewal, every cycle
Registrations tracked per product and market, and the post-market work that follows a device onto the market, each raised before it falls due.
Registrations per market
MHRA, TGA, Health Canada, EUDAMED and more, with registration numbers (licence numbers for Canada), renewal dates and holder details
Post-market surveillance
Reporting cycles start when a product goes on sale
Change assessments
Recorded against the product version they affect, whichever route applies; the route is your decision
Dossiers and audit programmes
Design dossier maintenance, and MDSAP, FDA inspection, notified body and ISO 13485 audits

03 · Documents and evidence
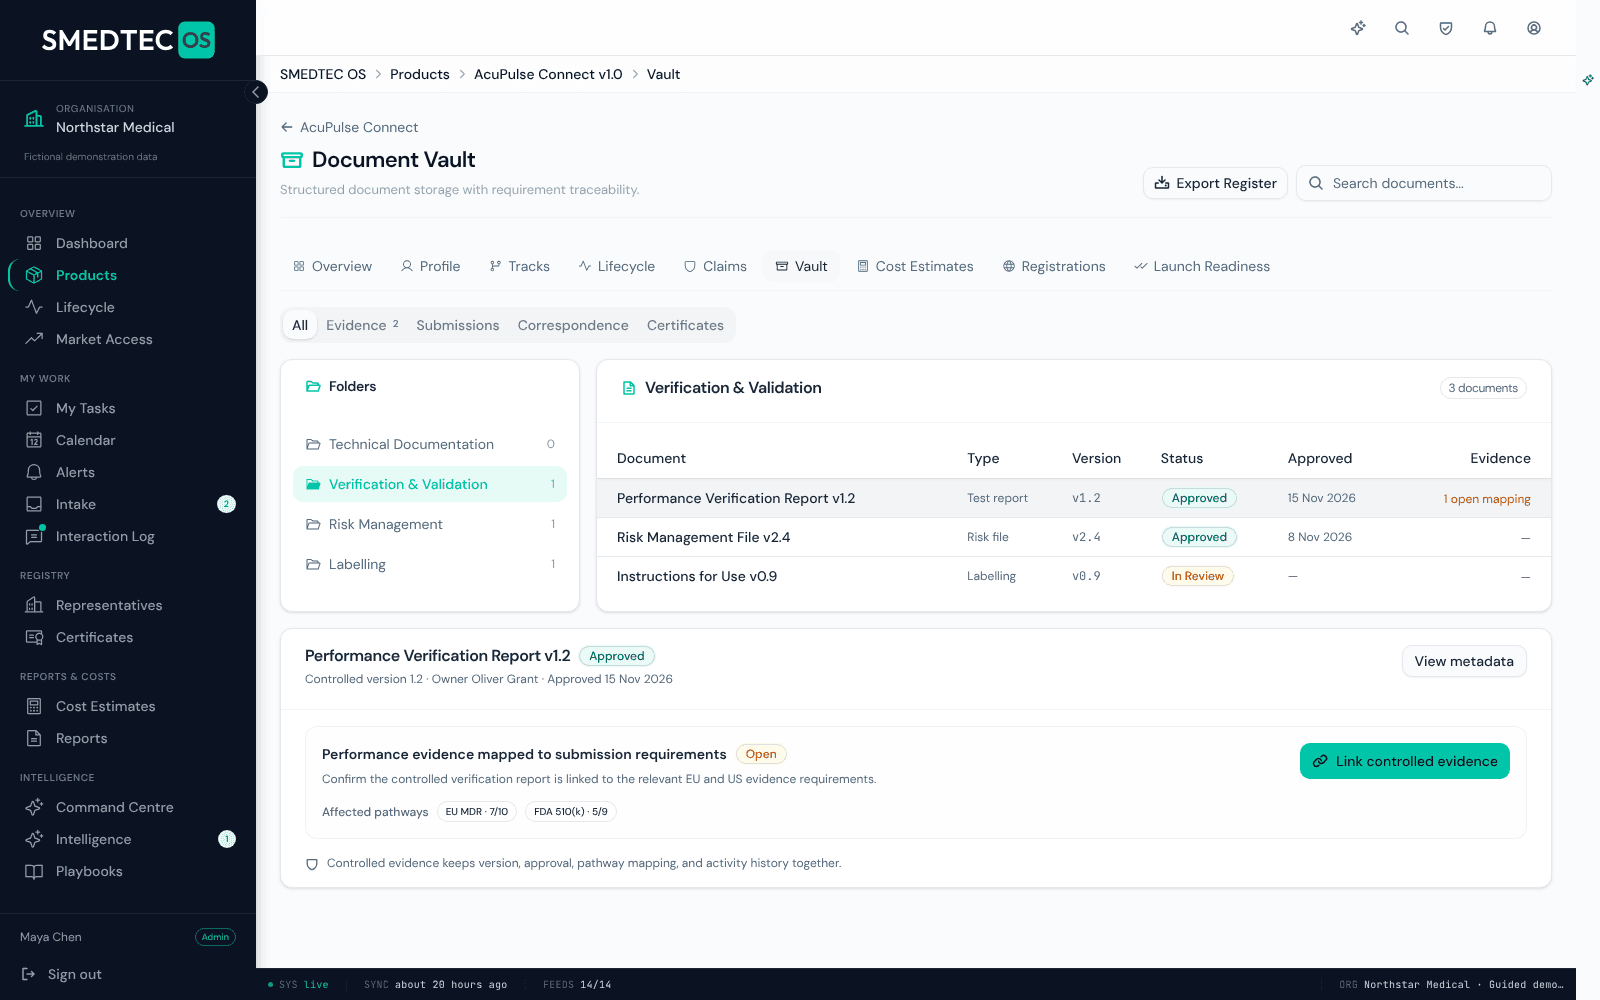
The documents behind every decision
A document vault for what your regulatory team owns, and audit packs an auditor can verify for themselves.
Document vault
Approvals, role-based access and supersession tracking
Verifiable audit packs
A SHA-256 manifest on every export
Intake portal
The rest of the business raises regulatory requests with provenance; AI-assisted triage turns them into tracked work in one step
Immutable activity log
Every upload, review and status change
04 · Advisers on your terms
Bring in your consultant or representative, and keep the record
Your workspace stays yours when you work with outside help. You decide who sees what, read-only, and for how long.
Invite advisers read-only
A consultant or representative joins by email as a viewer, scoped to the records you choose; viewers don't take one of your plan's seats
Remove them any time
Your records stay where they are
Connections you approve
If SMEDTEC represents or advises you, it asks to connect; you approve, switch on the products it sees one at a time, read-only, and end it whenever you like
On the record
A connection, and its ending, is recorded in your activity log
05 · Intelligence and Datum
Know what is changing, and ask your own record
A daily signal feed routed against your markets and device classes, and Datum, a workspace assistant that answers only from your own records and abstains when it has nothing to cite.
Regulatory developments
From MHRA, FDA, MDCG, the European Commission, TGA and more
Competitor clearances
510(k) clearances and PMA approvals from FDA, and records from BfArM, Swissmedic and EUDAMED
Market access
HTA and reimbursement decisions, the commercial signal most compliance tools omit
Predicates and standards
Predicates, adverse-event signals, FDA-recognised consensus standards and EMDN nomenclature
Datum answers with sources
It retrieves before it answers, cites what it used, and is scoped to your own organisation
SMEDTEC Intelligence
The free public digest at /intelligence
06 · Security and trust
Built to hold up in front of a competent authority or a notified body
Tenant isolation is enforced in the database, not in application code, and the evidence for that claim is a structured test rather than a statement.
Isolation in the database
Row-Level Security on every multi-tenant table, with SECURITY DEFINER RPCs for privileged paths
Penetration tested
Direct-API RLS test, 1 April 2026: 15 of 15 cross-organisation and unauthenticated attempts refused; log retained and available under NDA
Tamper-proof audit trail
Written by database triggers (before and after snapshots, actor, timestamp) that application code cannot bypass
Checkable manifests
SHA-256 audit-pack manifests hashed in the browser at upload; an auditor can re-compute every digest
Encrypted, in London
Data at rest in eu-west-2 (London), AES-256; TLS 1.2+ and HSTS on every surface
Five enforced roles
Owner, Admin, Member, Viewer and Requester, enforced by RLS policies
Validation pack
Platform Validation Statement SMEDTEC-VAL-001 and a self-serve Validation Kit (VAL-000 to VAL-006) in the Trust Centre; DPA published at /dpa
Seven structural properties that matter in a procurement conversation
These are architectural facts about the platform, not positioning statements.
- 01
Multi-tenant isolation is enforced in the database
Not in middleware, not in application code. Every table carries Row-Level Security, and a structured penetration test of the production endpoint is what backs the claim.
- 02
Every export carries a SHA-256 manifest
Audit packs and vault downloads are tamper-evident. An authority or notified body can re-compute every digest and confirm no file changed after export.
- 03
Your company owns its workspace
Your records sit in your own isolated workspace and remain your company's property under our terms. An adviser sees only the records you choose, read-only, and loses access the moment you remove it.
- 04
The intake portal is a first-class citizen
Sales, engineering and marketing raise regulatory requests with full provenance from submission through triage to tracked work.
- 05
AI that retrieves before it speaks
Datum and Briefing Studio work from recorded evidence, cite it, and abstain or flag when it is missing. Every call is token-capped and logged per organisation.
- 06
Human-readable entity references throughout
Sequential identifiers appear in every report, export and external communication, so a piece of evidence means the same thing in a notified-body submission as it does in the platform.
- 07
Built and used inside a working regulatory consultancy
SMEDTEC advises manufacturers through EU MDR transitions, 510(k) submissions and notified-body audits, and holds UK RP mandates itself. It runs that work on SMEDTEC OS; the entity model and terminology come from it.
Five roles. Distinct permissions. Enforced at every layer.
Every role is defined in the database and enforced by Row-Level Security policies — not by application checks that can be bypassed.
| Role | Typical user | Access scope |
|---|---|---|
| Owner | Founder, RA Director | Everything in the organisation, including billing and plan management. |
| Admin | RA Manager, Quality Manager | Full operational access including team management; no billing. |
| Member | RA Specialist, Quality Engineer | Full operational access to products, pathways, evidence and reports; no team management. |
| Viewer | Auditor, executive observer, outside consultant or representative | Read-only, scoped to the records you choose. |
| Requester | Sales, engineering, marketing | Intake portal only — submit and track their own regulatory requests. |
What SMEDTEC OS is not
It is not an eQMS. There is no CAPA, complaints handling or training-record management. SMEDTEC OS is the regulatory operations and intelligence layer that sits alongside the quality system you already run, and complements it rather than replacing it.
Is SMEDTEC OS one product or several?
One workspace with layers: the product record and pathways, registrations and post-market, documents and evidence, advisers on your terms, and intelligence. Every workspace has its own audit trail, document vault and assistant, kept to its own organisation.
Does the AI see data from other organisations?
No. Every retriever is scoped to the calling organisation at the database level. Datum answers only from your own vault, products and registrations, cites what it used, and abstains when it has nothing to cite.
How do you evidence the security claims?
A structured direct-API penetration test of Row-Level Security was run against the production endpoint on 1 April 2026 — 15 of 15 cross-organisation and unauthenticated attempts were refused, and the log is available under NDA. The platform validation statement and the self-serve validation kit are available in the Trust Centre; the DPA is published.
Which certifications do you hold?
SMEDTEC OS runs on SOC 2 audited infrastructure and its controls are mapped to ISO 27001:2022, with ISMS documentation published. We do not currently hold our own ISO 27001 or SOC 2 certificate and do not claim one.
See it with your own devices.
Start a free 14-day trial of your own workspace, or take the four-minute interactive demo on fictional data first.